Telegram Abuse: $4.5 Million Worth of Stars Exploited in Major Vulnerability Scheme
An Arabic-speaking hacker exploited a Telegram Stars loophole for two months, stealing $4.5M in digital stars and laundering $1.5M through rare NFT gifts like Plush Pepe before getting caught.
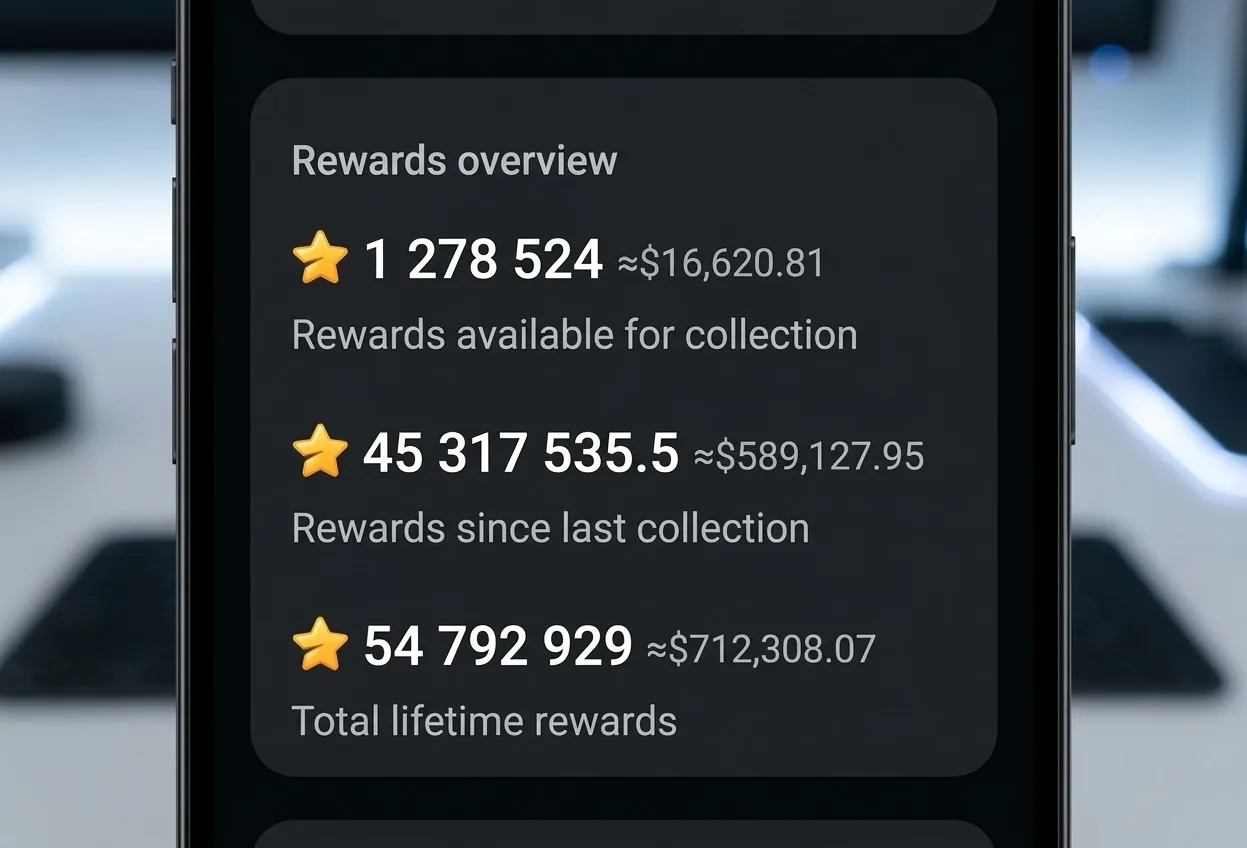
An Arabic-speaking user exploited a critical vulnerability in Telegram's payment and digital gift infrastructure, generating approximately $4.5 million USD worth of Telegram Stars over a two-month period. Before system operators intervened, the bad actor successfully cashed out over $1.5 million USD.
How the Telegram Stars Exploit Worked
The attack exploited a flawed transaction loop involving bot payments and high-value in-app NFT gift purchases:
- Initial Deposit: The user funded their balance with Telegram Stars via a standard bot payment gateway.
- The Refund Loop: The attacker attempted to purchase top-tier digital NFT gifts priced at 100,000 stars each. A system bug triggered an immediate transaction refund while still crediting the purchase or failing to revoke the balance properly.
- Infinite Re-use: Following each failed or refunded transaction, approximately 80,000 stars remained available in the user's account balance.
- Capital Compounding: By repeatedly executing this loop over two months, the attacker continuously inflated their Stars balance without adding new real-world capital.
Purchasing Rare "Plush Pepe" Digital Gifts
To launder and store value from the exploit, the participant bought rare collectible items across the platform.
- High-End Acquisitions: A significant portion of the illicit balance was converted into exclusive Telegram gifts, including three rare "Plush Pepe" items featuring black backgrounds.
- Off-Chain vs. On-Chain Risk: Unlike blockchain-verified assets, these in-app collectibles remained stored within Telegram's centralized application database.
System Crackdown and Permanent Asset Losses
Telegram has since patched the refund loophole and frozen the accounts involved, effectively stripping the perpetrators of their trading and transfer privileges.
Because the attacker kept items like PlushPepe-84 stored directly on their centralized Telegram account rather than minting and transferring them to a decentralized wallet on The Open Network (TON), the asset was frozen along with the account. PlushPepe-84 is now considered irretrievably lost.